Use Kali Linux like a professional pentester
From lab setup and reconnaissance to exploitation, post-exploitation, and client-ready reports — every skill is taught the way senior pentesters actually work it, command by command.
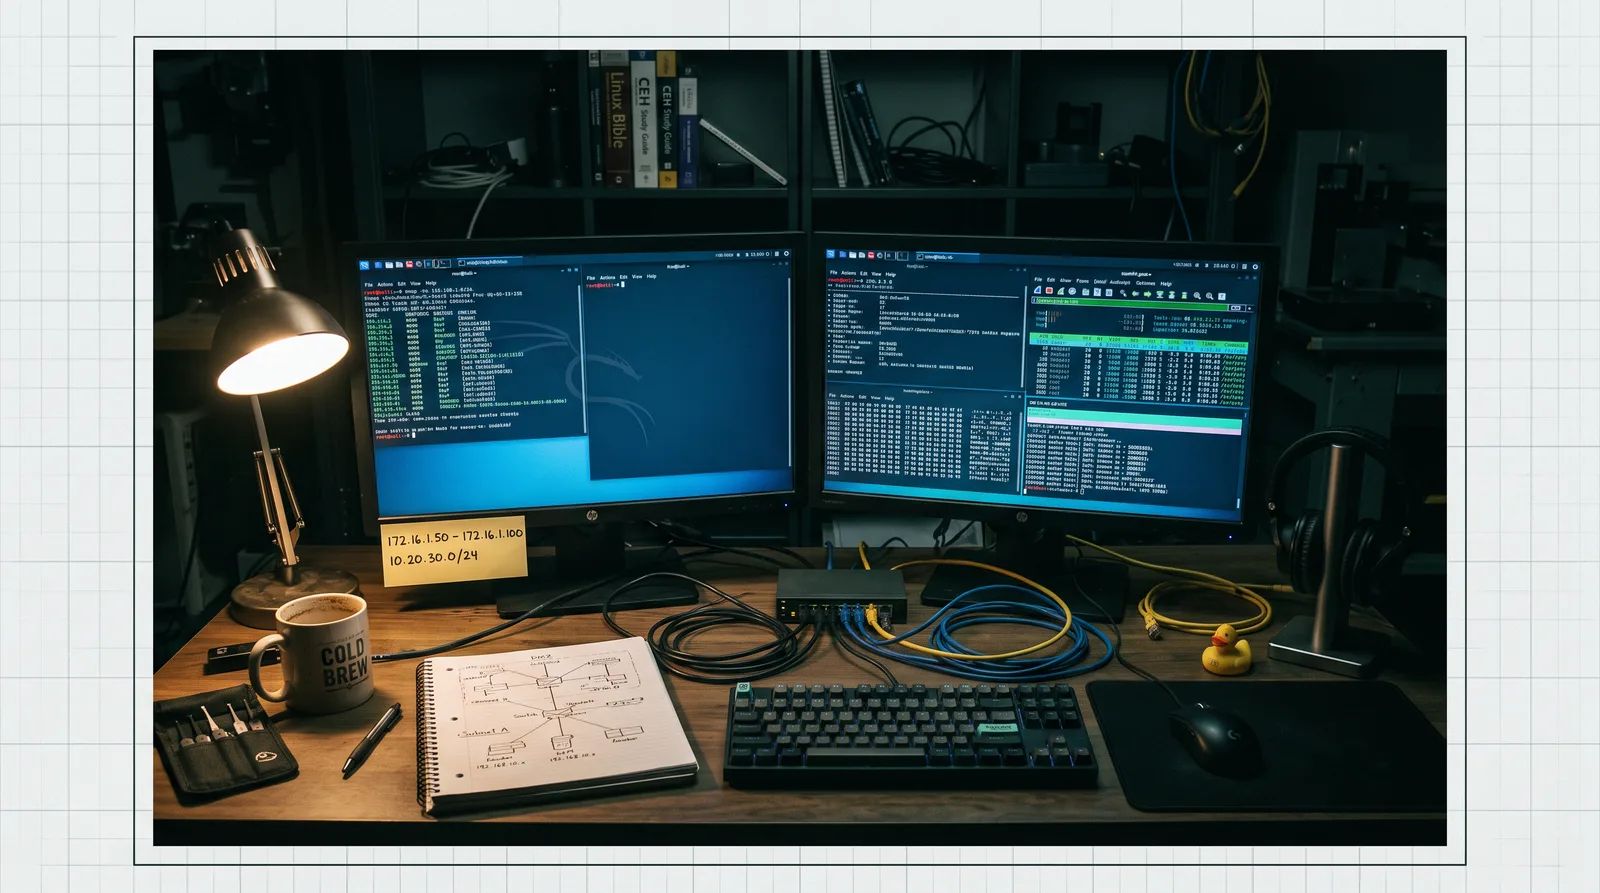
"A finding you can't explain clearly is a finding that doesn't get fixed — so we treat reporting as a technical skill, not an afterthought."
— Scott Edwards
What you'll learn
What you'll be able to do
- Set up and configure a professional Kali Linux environment with custom tool repositories and secure networking
- Conduct structured reconnaissance using Nmap, Maltego, and OSINT frameworks to map a target's attack surface
- Exploit common vulnerabilities with Metasploit, Burp Suite, and manual techniques against web apps and network services
- Perform post-exploitation tasks including privilege escalation, lateral movement, and credential harvesting in lab environments
- Use forensic and password-cracking tools such as Hashcat, John the Ripper, and Autopsy in investigative workflows
- Write clear, professional penetration testing reports that document findings, risk ratings, and remediation steps
How it works
A school that adapts to you
This isn't a set of static videos. Every lesson is generated live and tuned to where you actually are.
We learn your level
A quick placement check tailors your starting point so you're never bored or lost.
Lessons adapt as you go
Each lesson is written for your pace and your goal, adjusting as your skills grow.
Your AI coach keeps you moving
Checkpoints, feedback, and gentle nudges turn progress into a real result.
The curriculum
What's inside your school
0 modules · 0 lessons
Kali Linux Environment Setup & Configuration
Build a professional, secure Kali Linux workspace ready for real penetration testing engagements.
- 1.1Installing Kali Linux: VMs, Bare Metal, and WSLIncluded
- 1.2System Hardening and Secure NetworkingIncluded
- 1.3Managing Tool Repositories and Custom PackagesIncluded
- 1.4Building Your Lab: Target Machines and Isolated NetworksIncluded
- 1.5Professional Workflow: Notes, Version Control, and Engagement HygieneIncluded
Reconnaissance and Attack Surface Mapping
Systematically gather intelligence on a target using passive OSINT and active scanning techniques.
- 2.1The Penetration Testing MethodologyIncluded
- 2.2Passive OSINT with Maltego and Open-Source FrameworksIncluded
- 2.3Active Scanning with Nmap: Hosts, Ports, and ServicesIncluded
- 2.4OS Fingerprinting, Version Detection, and NSE ScriptsIncluded
- 2.5Synthesizing Recon Data into a Target ProfileIncluded
Vulnerability Assessment and Exploitation
Identify, validate, and exploit vulnerabilities in network services and web applications with industry-standard tools.
- 3.1Vulnerability Scanning with OpenVAS and NiktoIncluded
- 3.2Exploitation Fundamentals with Metasploit FrameworkIncluded
- 3.3Web Application Attacks with Burp SuiteIncluded
- 3.4Manual Exploitation: SQLi, XSS, and Command InjectionIncluded
- 3.5Exploiting Network Services: SMB, FTP, and SSH WeaknessesIncluded
Post-Exploitation: Escalation, Movement, and Harvesting
Maximize access after initial compromise through privilege escalation, lateral movement, and credential theft.
- 4.1Maintaining Access: Shells, Meterpreter, and PersistenceIncluded
- 4.2Privilege Escalation on Linux TargetsIncluded
- 4.3Privilege Escalation on Windows TargetsIncluded
- 4.4Lateral Movement and Pivoting Through NetworksIncluded
- 4.5Credential Harvesting and DumpingIncluded
Password Cracking and Digital Forensics
Apply cracking and forensic tools to recover credentials and investigate evidence in real-world workflows.
- 5.1Password Cracking with Hashcat: Wordlists, Rules, and MasksIncluded
- 5.2John the Ripper for Diverse Hash Types and File FormatsIncluded
- 5.3Wireless Network Attacks with Aircrack-ngIncluded
- 5.4Digital Forensics Fundamentals with AutopsyIncluded
- 5.5Memory Forensics and Log AnalysisIncluded
Penetration Testing Reporting and Professional Practice
Translate technical findings into polished, actionable reports that meet client and employer expectations.
- 6.1Anatomy of a Professional Pentest ReportIncluded
- 6.2Risk Ratings: CVSS Scoring and Business ImpactIncluded
- 6.3Documenting Evidence: Screenshots, Logs, and Proof-of-Concept CodeIncluded
- 6.4Writing Remediation Recommendations That Get ImplementedIncluded
- 6.5Legal, Ethical, and Scoping EssentialsIncluded
Who it's for
Is this you?
Aspiring pentesters
You want your first offensive security role and need hands-on, methodology-driven skills that hold up in interviews and on the job.
IT admins going offensive
You manage systems and networks daily and want to understand how attackers see your infrastructure — from the outside in.
Career-changers into cybersecurity
You're transitioning from another field and need a structured, no-fluff path through Kali's real-world toolset to become job-ready.
Certification candidates
You're prepping for CEH, PenTest+, or OSCP and want practical, command-level fluency that makes exam scenarios click.
Junior security analysts
You're already in a security role but want to level up from defensive monitoring to hands-on exploitation and professional reporting.
Freelance security consultants
You take on small security engagements and need to tighten your methodology, reporting quality, and legal/scoping practices.
Questions
Frequently asked
Your teacher
A note from your teacher
Scott Edwards
If you've opened Kali Linux, stared at the application menu, and wondered where to actually start — I've been there. Not as a beginner forever, but as someone who remembers exactly what it felt like to run a tool, get output, and have no idea what to do with it next. That gap between "I have Kali installed" and "I know how to run a professional engagement" is real, it's common, and it's what this school is designed to close.
I built this curriculum the way I wish someone had taught me: methodically, in the order a real penetration test actually unfolds. We start with your environment — because a sloppy lab produces sloppy habits — and we end with your report, because a finding you can't communicate clearly might as well not exist. Everything in between follows that same logic. Each tool is introduced when you need it, explained in terms of what it does to a target and why that matters, and practiced against machines you control in an isolated environment.
I want to be direct with you about something: this is not a course that teaches you to click buttons and memorize outputs. The cybersecurity job market is full of people who can launch a Metasploit module. Employers and clients are looking for professionals who understand what they're doing, can adapt when something doesn't work, and can document their findings in a way that gets vulnerabilities actually fixed. That's what we build here — technical fluency paired with professional practice.
The section most people tell me they didn't expect to need — and then realize they needed most — is the reporting module. CVSS scoring, business impact framing, writing remediation steps that a development team will implement rather than ignore: these are the skills that move you from "someone who hacks things in a lab" to someone who gets hired, retained, and trusted with real engagements. We cover it in depth, because it deserves that.
Whether you're pivoting into cybersecurity from IT, working toward your first pentesting role, or shoring up gaps in skills you already have, the work here is designed to matter beyond this course. Come ready to follow along in your lab, ask hard questions, and hold yourself to a professional standard. That's the standard I hold myself to in every lesson I write.
— Scott Edwards
Start your journey today
Get instant access — learn at your own pace with an AI coach in your corner.
$175/yr
Recurring billing · cancel anytime
Secure checkout · Instant access
- 6 modules, 30 lessons
- AI-adaptive lessons tuned to your level
- Quizzes & checkpoints to lock in progress
- Your own AI learning coach
- Learn on any device, at your pace
- Full access for as long as you're subscribed